
Anthropic "Mythos" Strikes Cybersecurity Sector, Bernstein: Don't Panic, You've Misread It

Anthropic's new model "Mythos" sparked a collective sell-off in the cybersecurity sector due to statements regarding its leap in "cybersecurity" capabilities. However, Bernstein Research quickly issued a clarification: investors misinterpreted the information. This neither signals Anthropic's entry into the cybersecurity software market nor undermines the structural tailwinds AI brings to the industry.
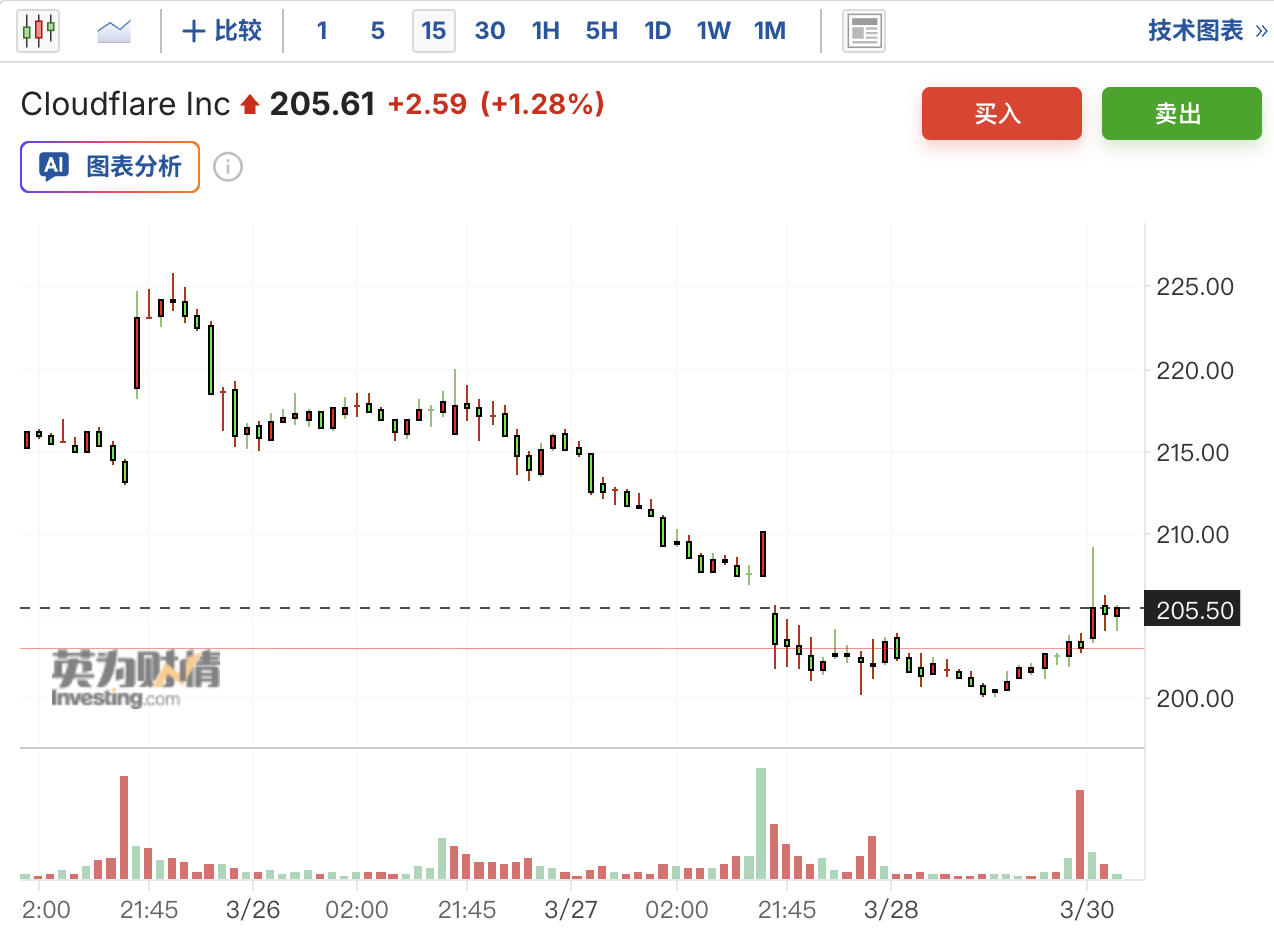
According to Fortune magazine’s report last Friday, Anthropic’s soon-to-be-released "Mythos" model promises "significantly higher scores" in software coding, academic reasoning, and cybersecurity testing. This wording triggered a market sell-off, with most cybersecurity stocks covered by Bernstein, such as Cloudflare, dropping 5% to 7%.
Bernstein analysts responded swiftly on the same day, pointing out that the cybersecurity-related aspects of "Mythos" are essentially routine enhancements to code security capabilities and proactive measures to prevent the product from being misused maliciously by Anthropic. Neither is in competition with the cybersecurity software industry, nor do they weaken the AI-driven demand logic for the sector.
Bernstein stated clearly in its report that it is maintaining the ratings, target prices, and financial forecasts for all its covered cybersecurity companies.
Where Did the Market Panic Come From?
The Fortune magazine report’s wording regarding the leap in "cybersecurity" capability became the direct trigger for the sell-off.
Investors interpreted this as two potential threats: one, Anthropic might directly enter the cybersecurity software market, creating competition with existing players; two, enhanced AI model capabilities could lower the intensity of cyber threats, thereby weakening demand for traditional security tools.
Bernstein analysts described investors as "predictable as clockwork," saying that whenever there’s mention of a step-change in cybersecurity capability, related software stocks are sold off en masse.
What Is Mythos Really Doing: Code Security and Abuse Prevention
Bernstein broke down the cybersecurity-related aspects of "Mythos" into two levels.
First is the enhancement of code security capabilities. Analysts believe this is a basic hygiene standard for the product and is a baseline expectation for Anthropic’s offerings, which will not limit the value of most other cybersecurity tools.
They’ve previously pointed out that software vulnerabilities account for a relatively small portion of security breaches, and the range of vendors directly affected by Claude’s code security features is likewise limited.
Second is the prevention of product abuse, which is the core logic of this release. The cybersecurity industry has well-documented cases where Claude, once compromised, could be used by threat actors to identify software vulnerabilities and quickly create targeted malware. These attacks often occur faster than vendors or users can patch the issue.
Additionally, attackers may use hacking techniques to hijack enterprise Agents built on Anthropic, carrying out lateral movement, account takeover, and data leakage within organizations.
Bernstein points out that addressing these risks is not new for Anthropic. The company has long discussed and proactively implemented safeguards. This release deepens that direction rather than marks a strategic shift.
The AI Tailwinds in Cybersecurity Remain Intact
Analysts rebutted the notion that "AI tailwinds are damaged" from two perspectives.
First, Anthropic is just one provider in the LLM market. There are numerous long-tail LLM vendors, and not all will proactively implement anti-abuse mechanisms like Anthropic.
More importantly, open-source LLMs are already widely circulated in an unregulated environment—even if they are less capable than Claude, they can still be effectively used by threat actors to create malware or launch phishing attacks.
Bernstein reminds that even without these tools, attackers are still successful in today’s landscape, which means attackers don’t need high-quality tools to gain additional leverage for attacks.
Second, AI’s upside for the cybersecurity sector largely comes from the emergence of new security solutions, rather than mere intensification of demand for existing tools.
Analysts noted that at this week’s RSA conference, almost every booth was focused on areas like Agentic SOC (intelligent security operations centers), Agent identity security, and Agent data security—emerging directions in cybersecurity.
These market opportunities won’t be affected by Anthropic increasing product security. Moreover, as most enterprises maintain technical neutrality toward LLMs, the demand for multi-Agent protection solutions will persist.
Disclaimer: The content of this article solely reflects the author's opinion and does not represent the platform in any capacity. This article is not intended to serve as a reference for making investment decisions.
You may also like
XRP Outperforms Bitcoin and Major Stocks Over 10 Years but Numbers Are Easy to Misread
Federal Reserve Chair Waller: Number of Rate-Setting Meetings Will Be Reduced in Coming Years
Federal Reserve Chair Walsh pointed out that although eight meetings per year is "an appropriate number" for the FOMC, starting in 2027, one meeting will focus on macro monetary policy strategy without interest rate voting or policy statement issuance. In 2028, such strategic meetings will increase to two, and the number of policy-setting meetings will be reduced correspondingly to six. Walsh stated that this adjustment aims to provide the committee with space to consider more long-term "major issues."
The Federal Reserve holds rates steady as expected, with divisions resurfacing but fewer hawkish voices; Cook and two other voting members support a rate hike.
After three dissenting votes in July, there was once again division in this rate decision, with two of the 12 FOMC members opposed, indicating a decrease in hawkish dissent. Among the dissenters, Harker had already voted against holding rates steady in July due to his support for a rate hike, while Cook’s dissent is seen as a rebuke to Trump’s attempt to remove her. This statement changed the description of the economy from “steadily expanding” to “strong expansion,” continued to emphasize that inflation remains high, and newly added that accumulating information will help determine the policy stance needed to ensure inflation returns to target in a timely manner. According to the “New Fed News Agency,” the Fed’s decision to hold rates steady aims to gain time to assess whether further rate hikes are necessary.
Crypto prices
More


